Move .env secrets off disk without breaking local development
Find plaintext secrets in .env files, secure them with 1Password Enterprise Password Manager, and keep using them as environment variables.
Bring local secret sprawl under control

Extend secret scanning beyond repositories
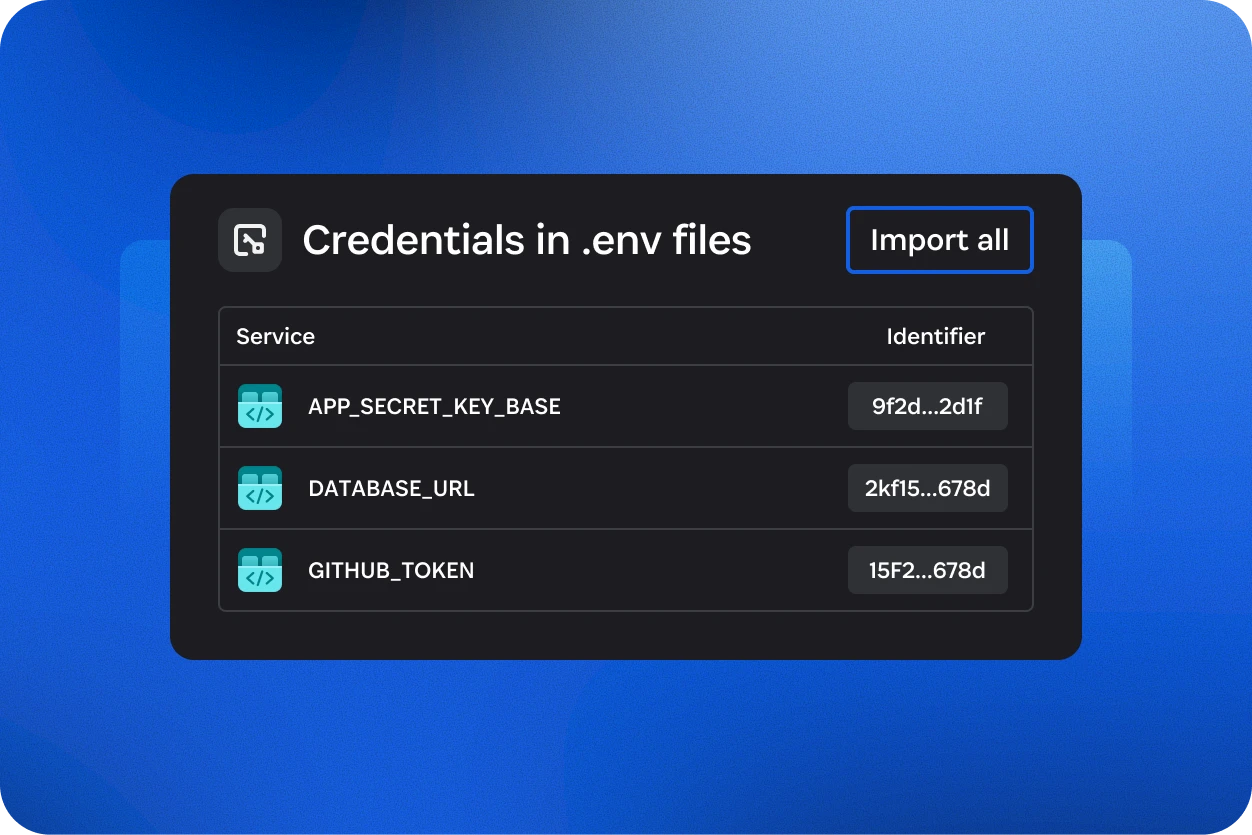
Developer Watchtower checks common development folders for plaintext secrets in .env files and SSH keys that repository scans may not see. The report identifies affected developers and devices without including secret values.

Prioritize the widest local exposure
See which secrets appear across the most developers and devices, so security teams can focus remediation where local exposure is greatest.

Keep plaintext .env values off disk
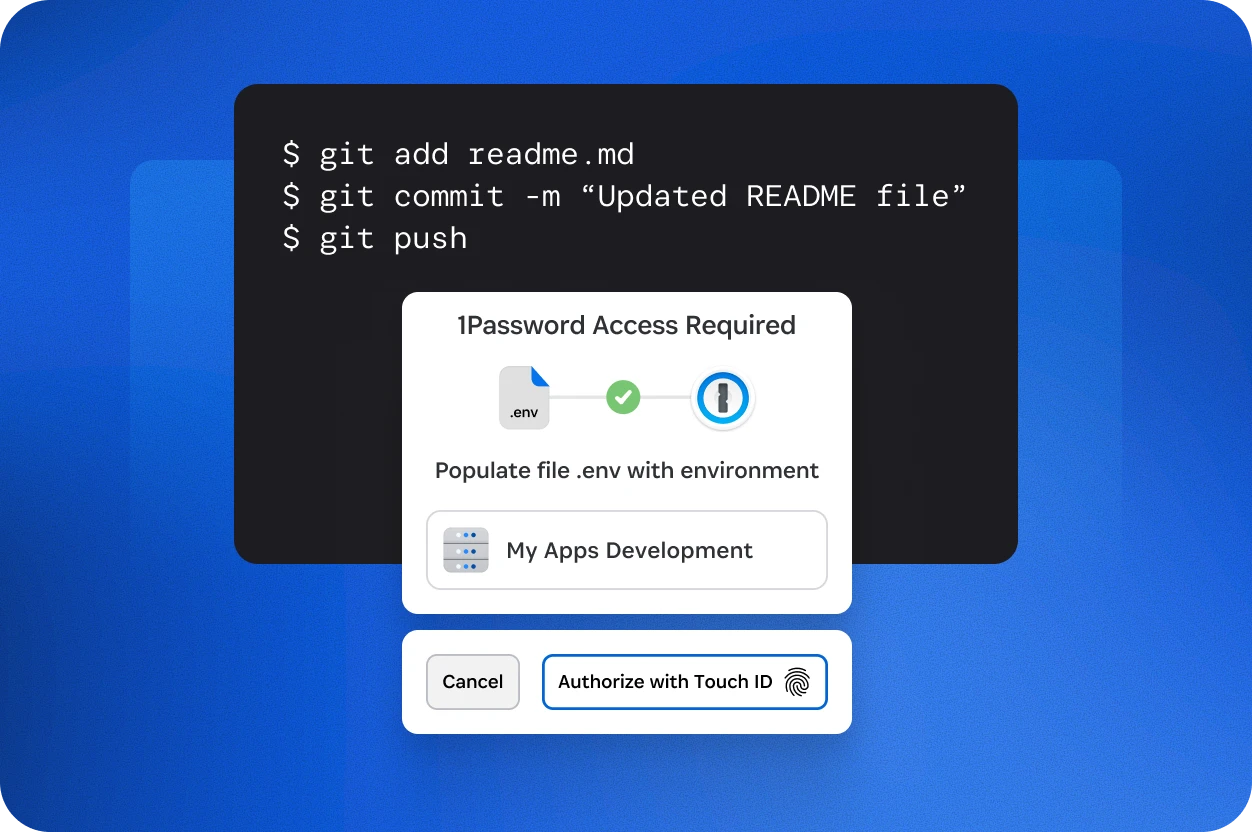
Developers can move .env values into 1Password and make them available to compatible applications at runtime through the same path (macOS and Linux only), without storing plaintext values on disk.
1Password helps you secure developer workflows
How Developer Watchtower works
Detect
Find secrets exposed in local .env files across developer devices
Store
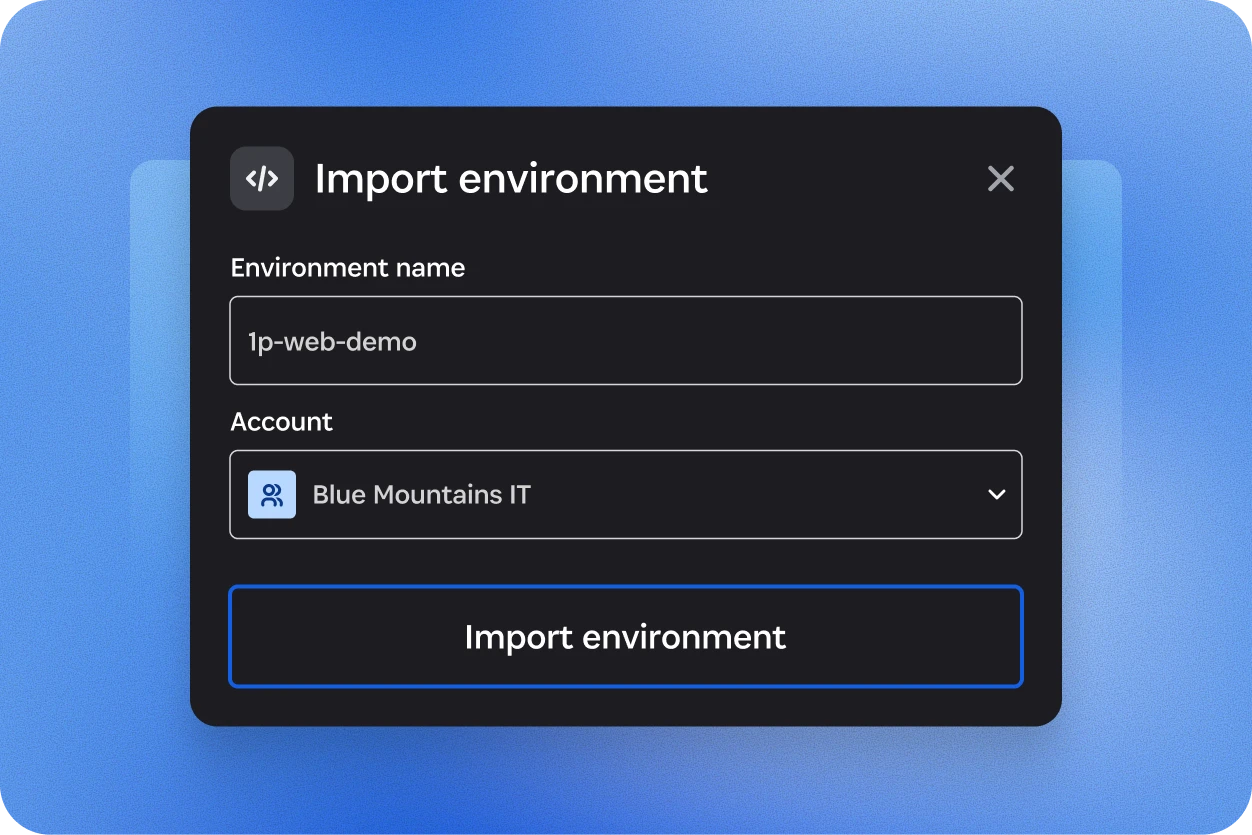
Move exposed values into 1Password Environments and remove plaintext copies from disk
Run
Keep existing workflows intact by mounting protected .env files where apps expect them
200,000+ businesses trust 1Password
Ready to secure your team like the best in the business?
Request a demo to see how 1Password governs every credential your company runs on, across employees, developers, machines, and AI agents.
Resources for getting started
How 1Password EPM protects developer secrets
See how teams secure API keys, SSH keys, and tokens across CI/CD pipelines and local machines.
Watch webinar
Total Economic Impact™ of 1Password Business
The ROI and efficiency gains realized by 1Password customers, according to Forrester.
Read analyst report
Independently tested, publicly proven
Independent firms pen-test and audit our apps, code, and infrastructure. We back a bug bounty of up to $1 million and hold SOC 2 Type 2, ISO 27001, and more.
View Security architectureDeveloper Watchtower FAQs
What is a .env file, and is every .env file risky?
A .env file is a simple text file that stores settings an application needs to run, and it may include API keys, database passwords, or cloud credentials. The file itself is not necessarily risky. The risk begins when real secrets sit inside it as readable plaintext on a device.