Compliance and cyber insurance
Simplify meeting your cybersecurity compliance and cyber insurance requirements. 1Password helps by mitigating credential risks, enforcing device compliance.
The implications of unauthorized access
Ransomware risks
In more than 92% of cases where attacks progressed to ransom stage, the attacker had leveraged unmanaged devices in the network.
Source: Microsoft Digital Defense Report, Microsoft Threat Intelligence, October 2024.
Non-compliance costs
There’s been more than $5.3 billion in total GDPR fines as of October 2024.
Source: GDPR Enforcement Tracker, October 2024.
Data breaches
68% of breaches involved a human element such as compromised user credentials or phishing.
Source: Verizon Data Breach Report, May 2024
Navigate compliance complexity
Credential risk management
Device compliance enforcement
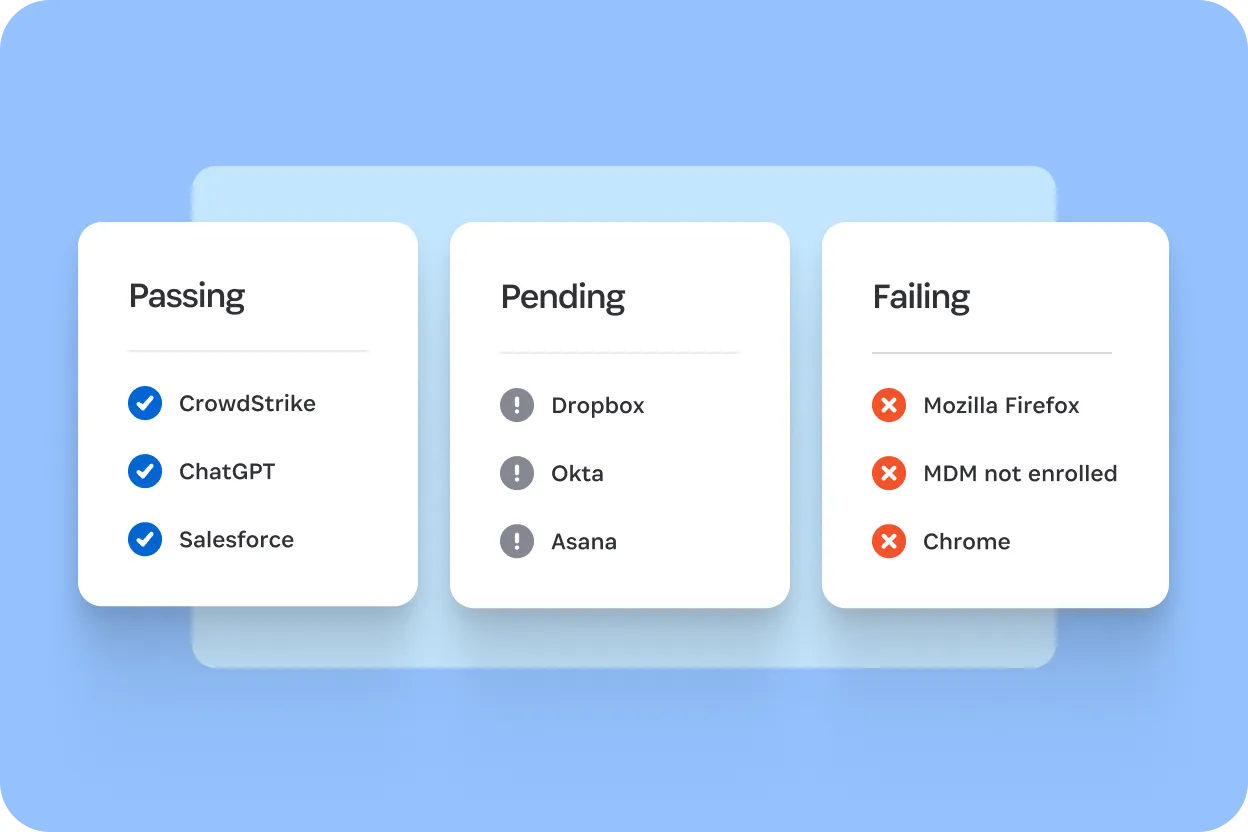
SaaS security and visibility
Close the Access-Trust Gap
Granular access controls
Add custom groups based on department roles or functions and apply permissions based on those job functions.
Multi-factor authentication (MFA)
Add strong, unique passwords, passkeys or MFA where SSO doesn’t cover sign-ins.
Contextual access policies
Allow or block sign-ins based on device compliance at the time of login.
"Being able to track and trace (within limits) who accesses what, where, and how is a big deal, especially in reporting and auditing after the fact."
Lee Jon Scramstad
Systems Architect, Synex
Resources for getting started
More than compliance
Regulations are necessary, but security goes beyond merely meeting compliance requirements.
Learn more
Simplify regulatory compliance
Simplify compliance cybersecurity risks with access controls, visibility, and auditing.
Watch the webinarCybersecurity compliance FAQs
What is cybersecurity compliance, and why does it matter?
Cybersecurity compliance refers to meeting regulatory requirements and cybersecurity frameworks designed to protect sensitive data and prevent breaches. ISO 27001, SOC 2, NIST, HIPAA, GDPR and DORA are cybersecurity regulations and frameworks that can help organizations implement controls to safeguard data, enforce access controls, and prevent data breaches.
How does 1Password help with ISO 27001, SOC 2, and other compliance standards?
Why do cyber insurers care about credential security, device trust, and application access?
How can 1Password help reduce cyber insurance premiums?
What’s the best way to protect against ransomware and credential‑based attacks?
Simplify compliance requirements
Reduce risk and enforce policy based on compliance across the business.