Cloud Privileged Access for humans and AI agents
Zero standing privilege enforced through just‑in‑time, and just‑enough access
The companies putting AI agents to work are securing them with 1Password
Standing access turns AI agent growth into security risk
96%+of standing access sits unused
Source: Gartner, Innovation Insight for Cloud Infrastructure Entitlement Management88%of breaches exploit existing access
Source: Verizon DBIR 2025From standing access to zero standing privileges
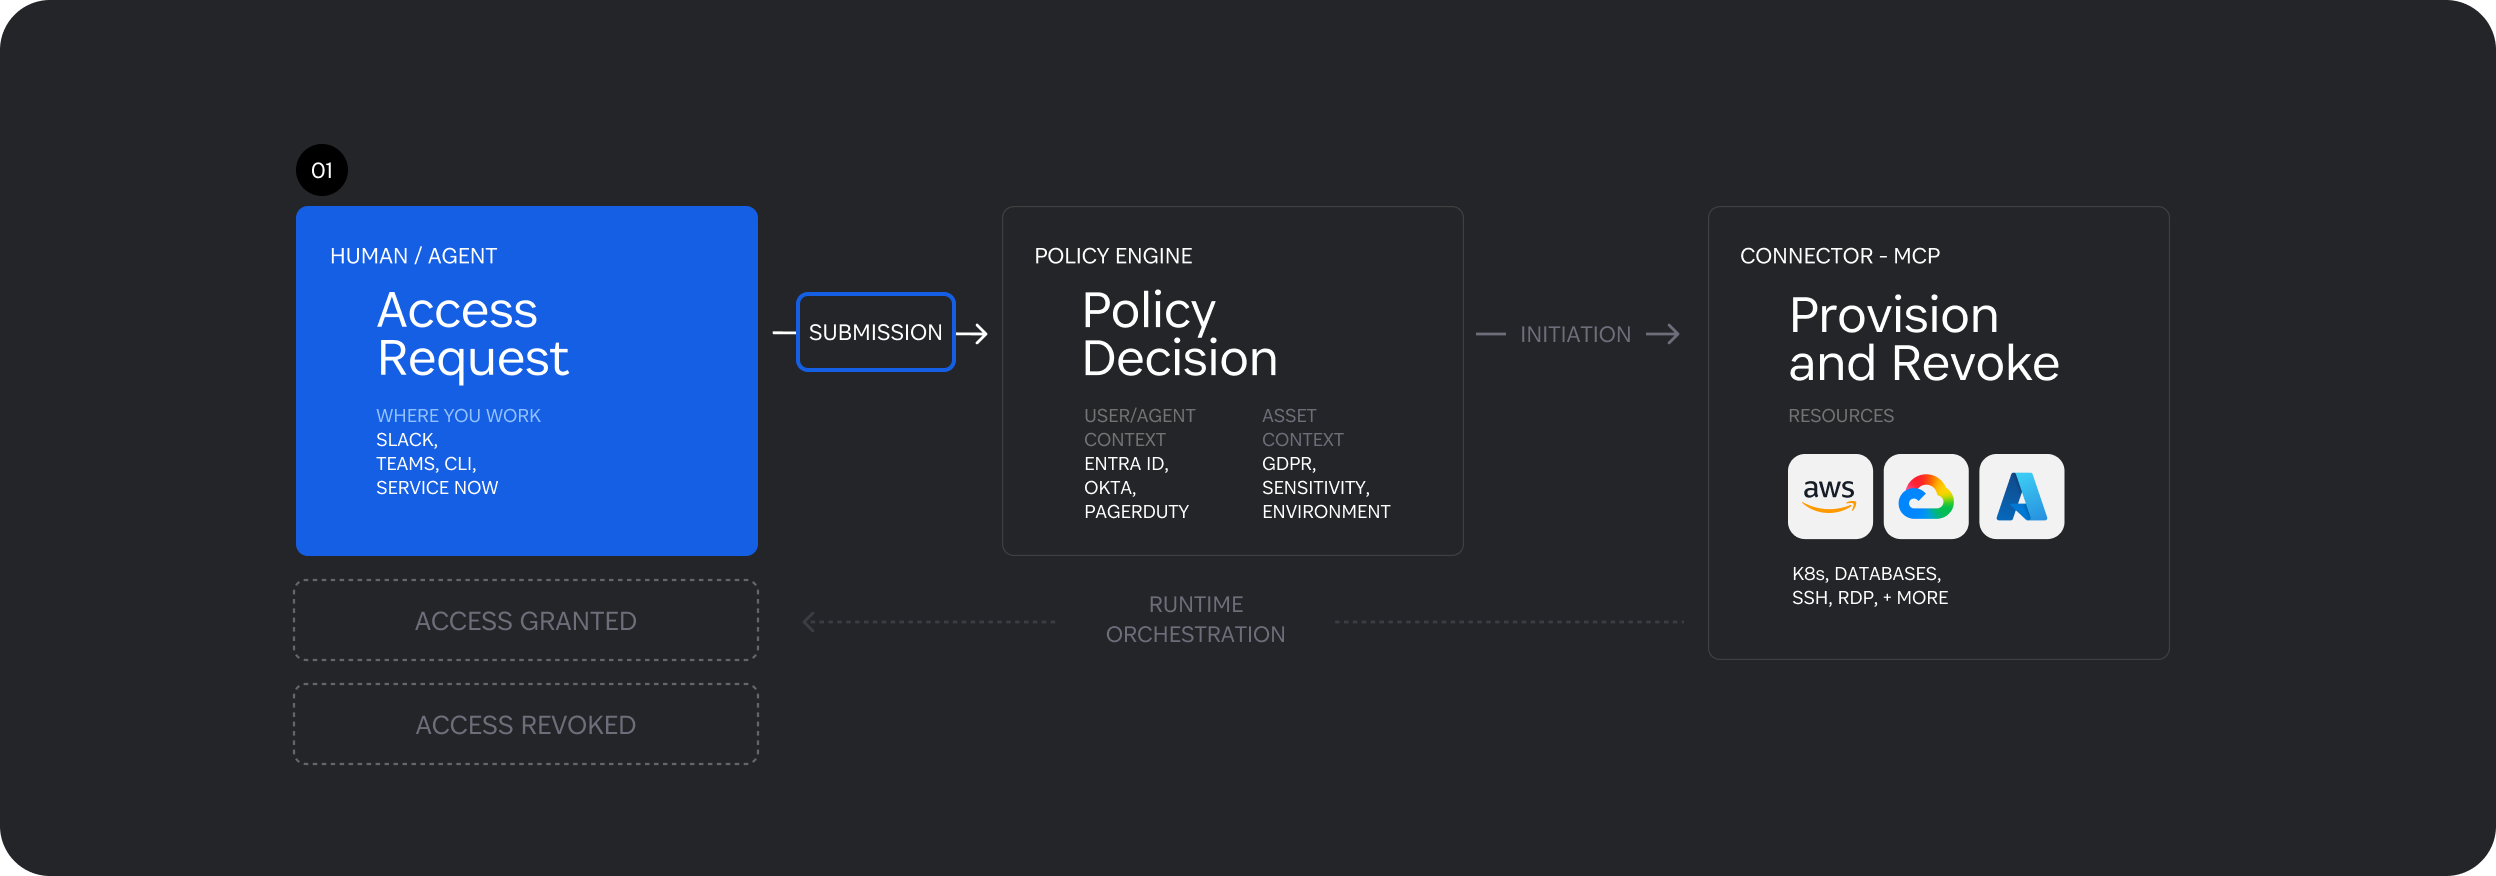
01. Request access where work happens
Users request access from Slack, Teams, the CLI, or ServiceNow, for themselves or their agents. Every request is tied to an intended action instead of relying on invisible standing privilege.
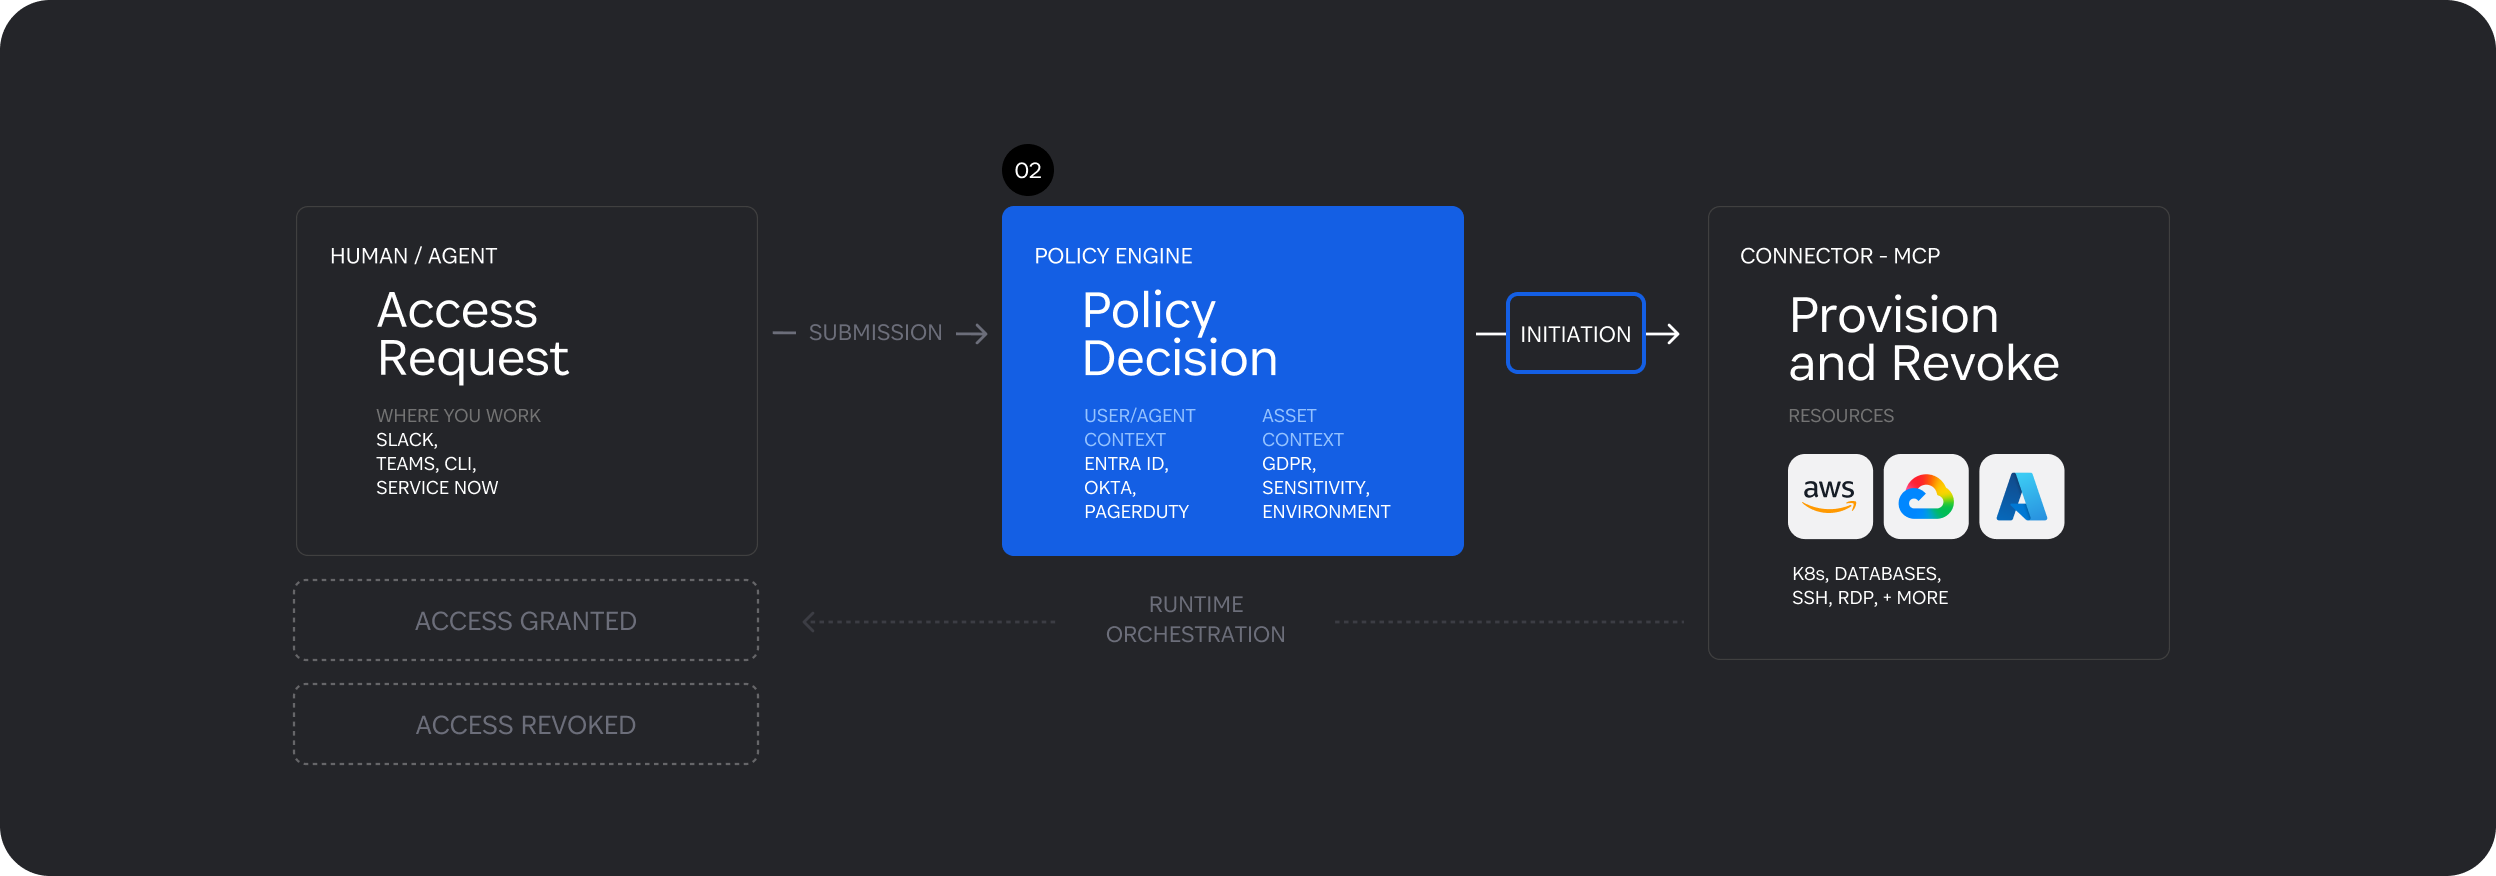
02. Evaluate every request in context
Policy decisions draw from Entra, Okta, PagerDuty, asset context, and sensitivity. Every request is evaluated at the moment it arrives, automatically or with a human in the loop depending on your approach.
03. Provision minimum access, just in time
A lightweight connector in your environment provisions just-in-time, just-enough access to Cloud Infra, K8s, databases, SSH, RDP, and more. Agents connect via MCP. Everything is scoped to need and policy.
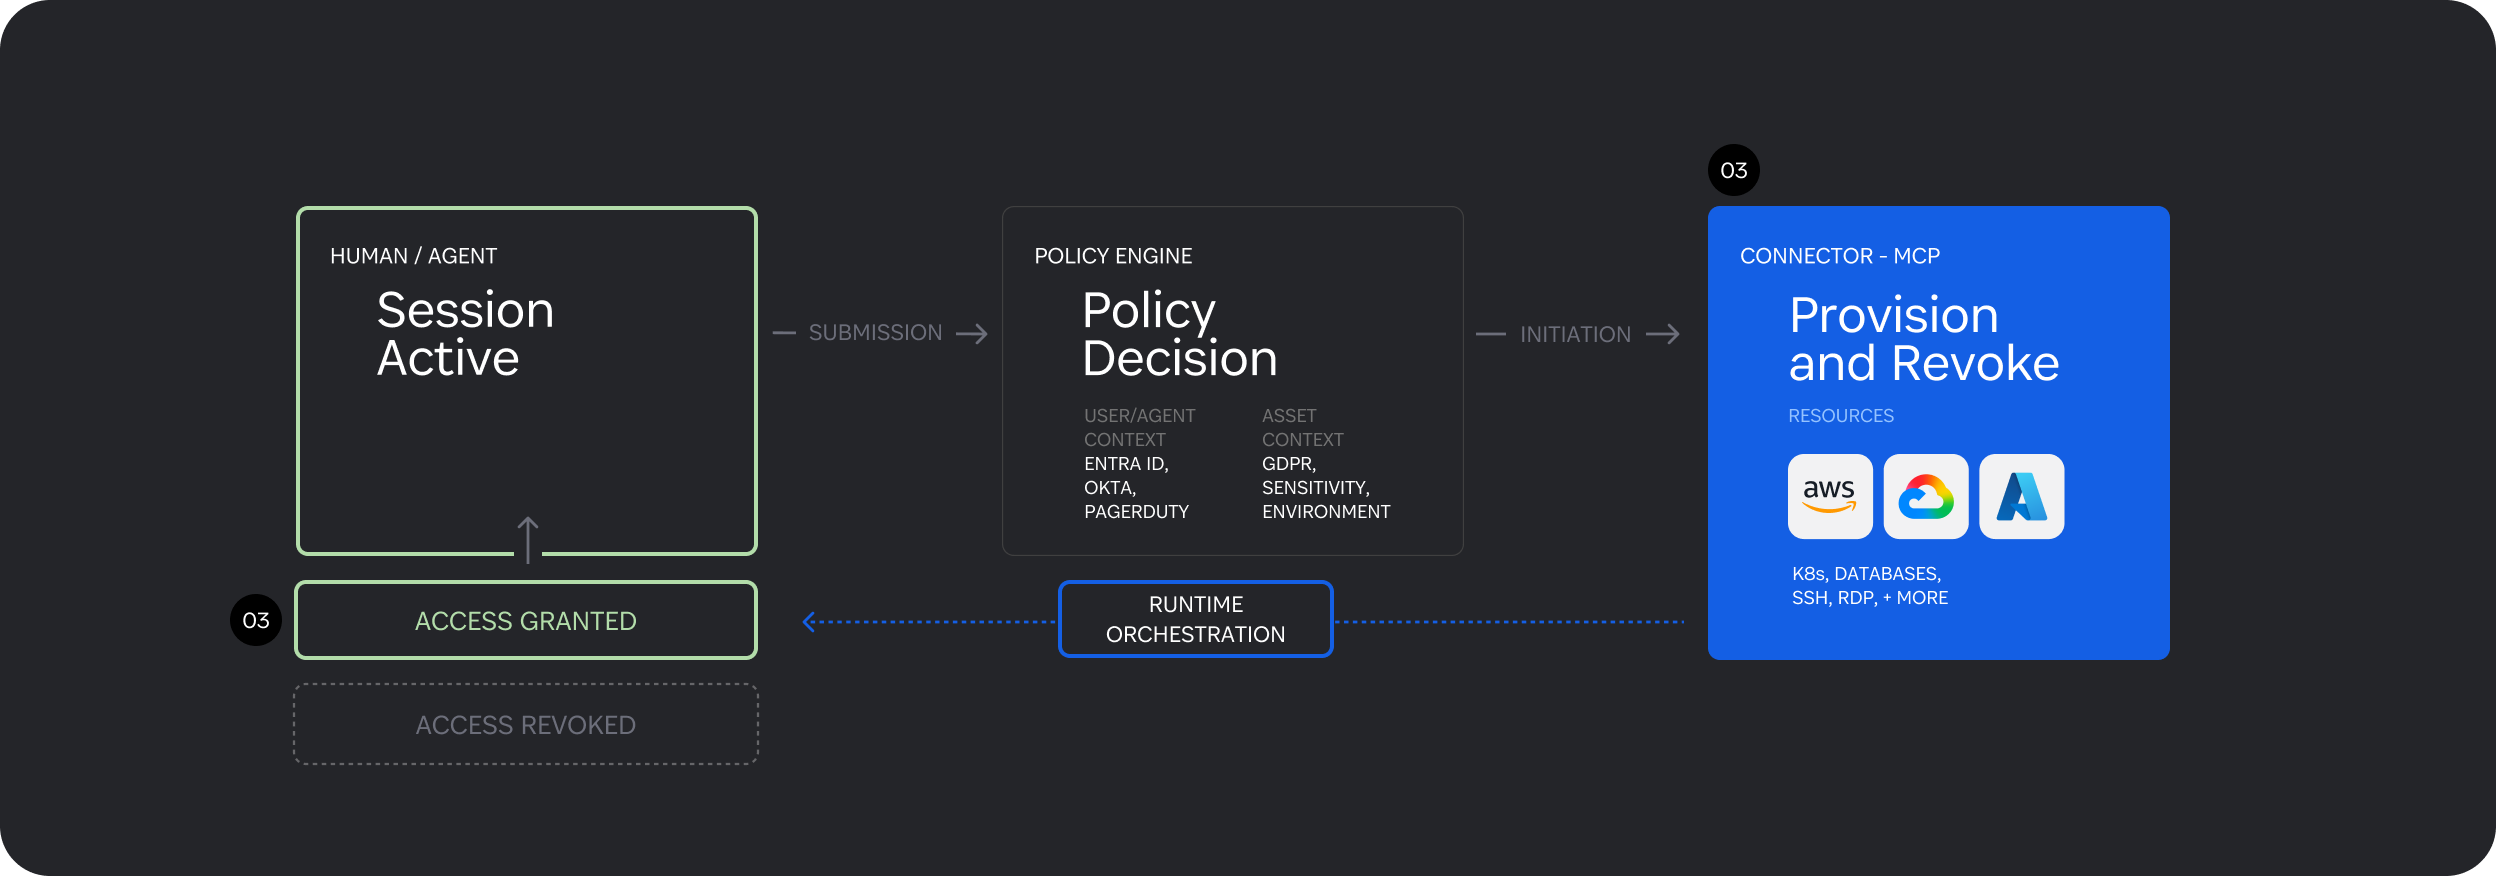
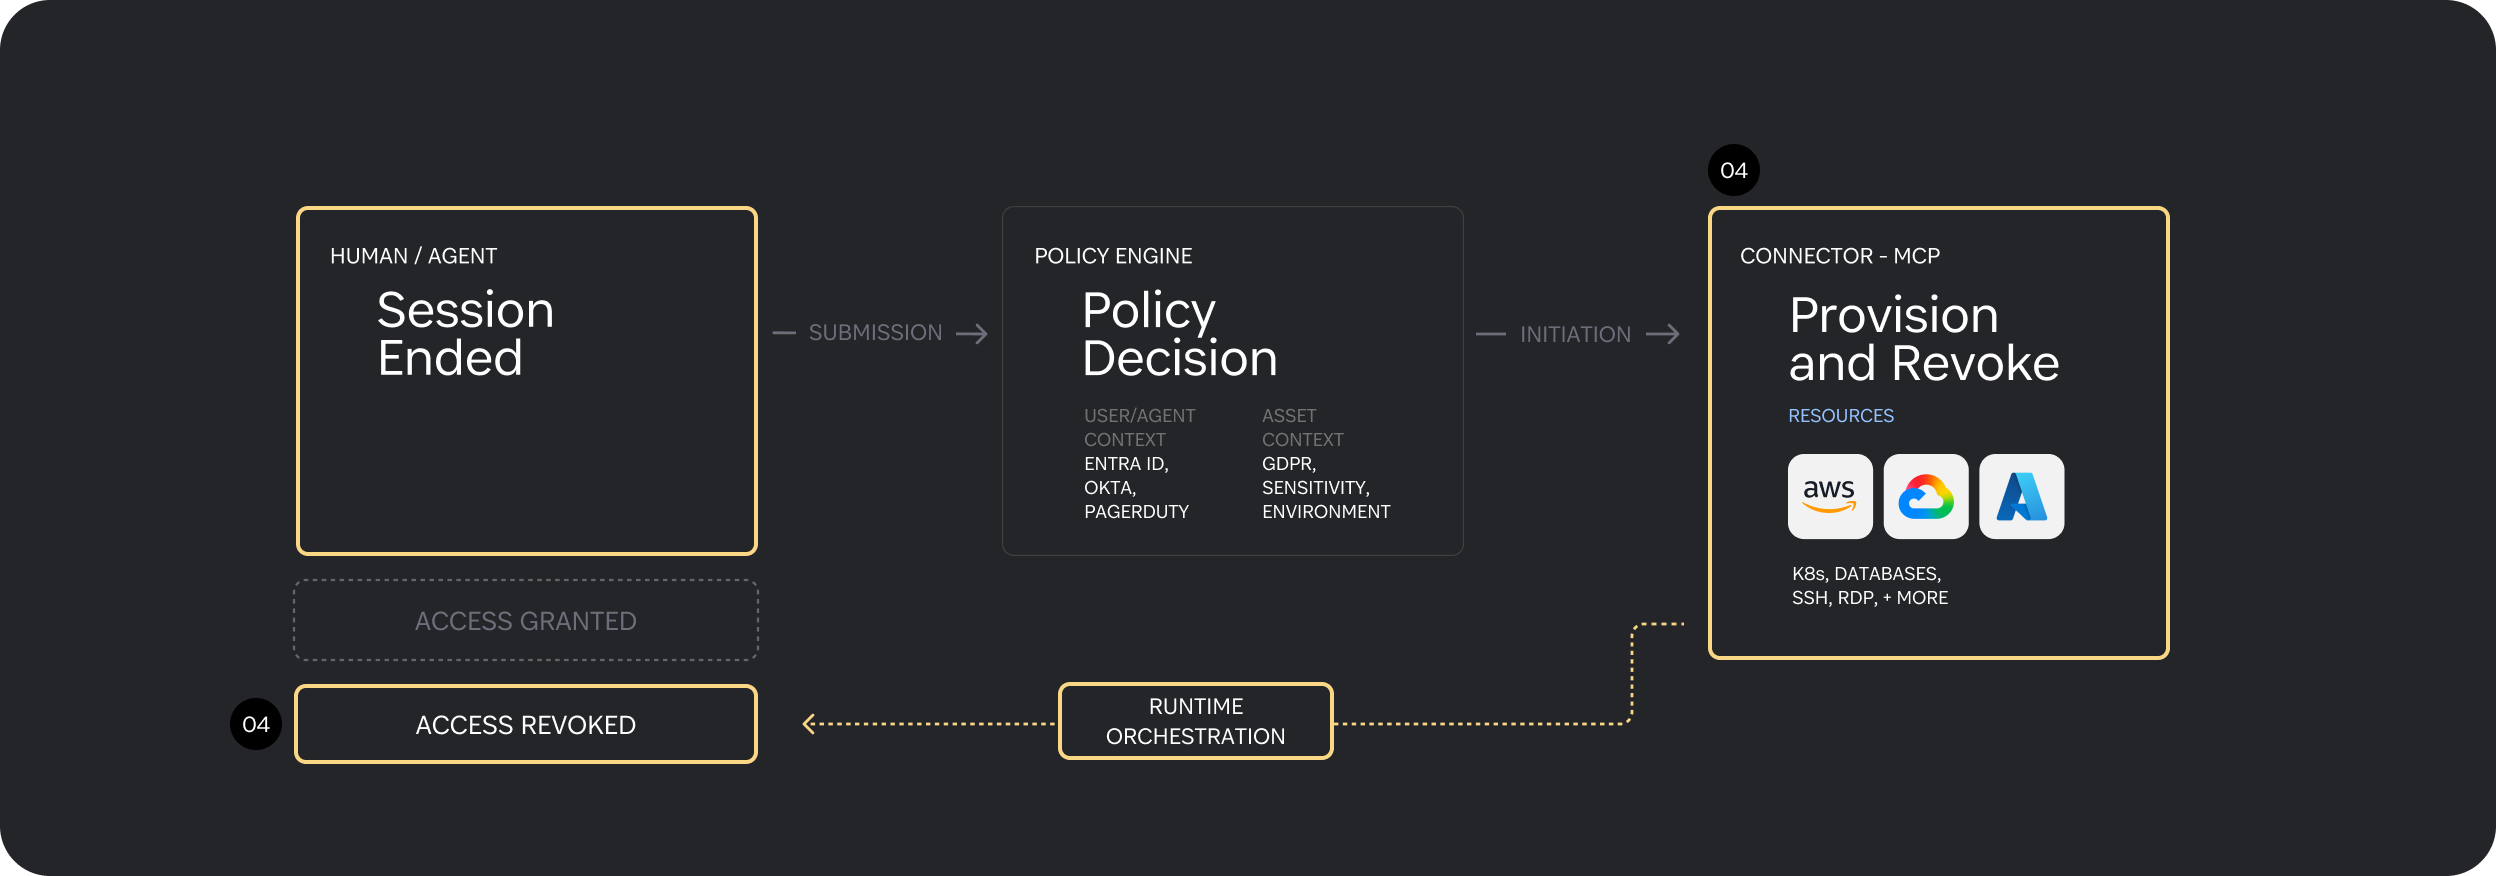
04. Every decision leaves a trail
When a session ends or risk changes, access is revoked. Every request, decision, and revocation is captured with context and surfaced through the audit log and SIEM integration, so teams can see what happened and why.
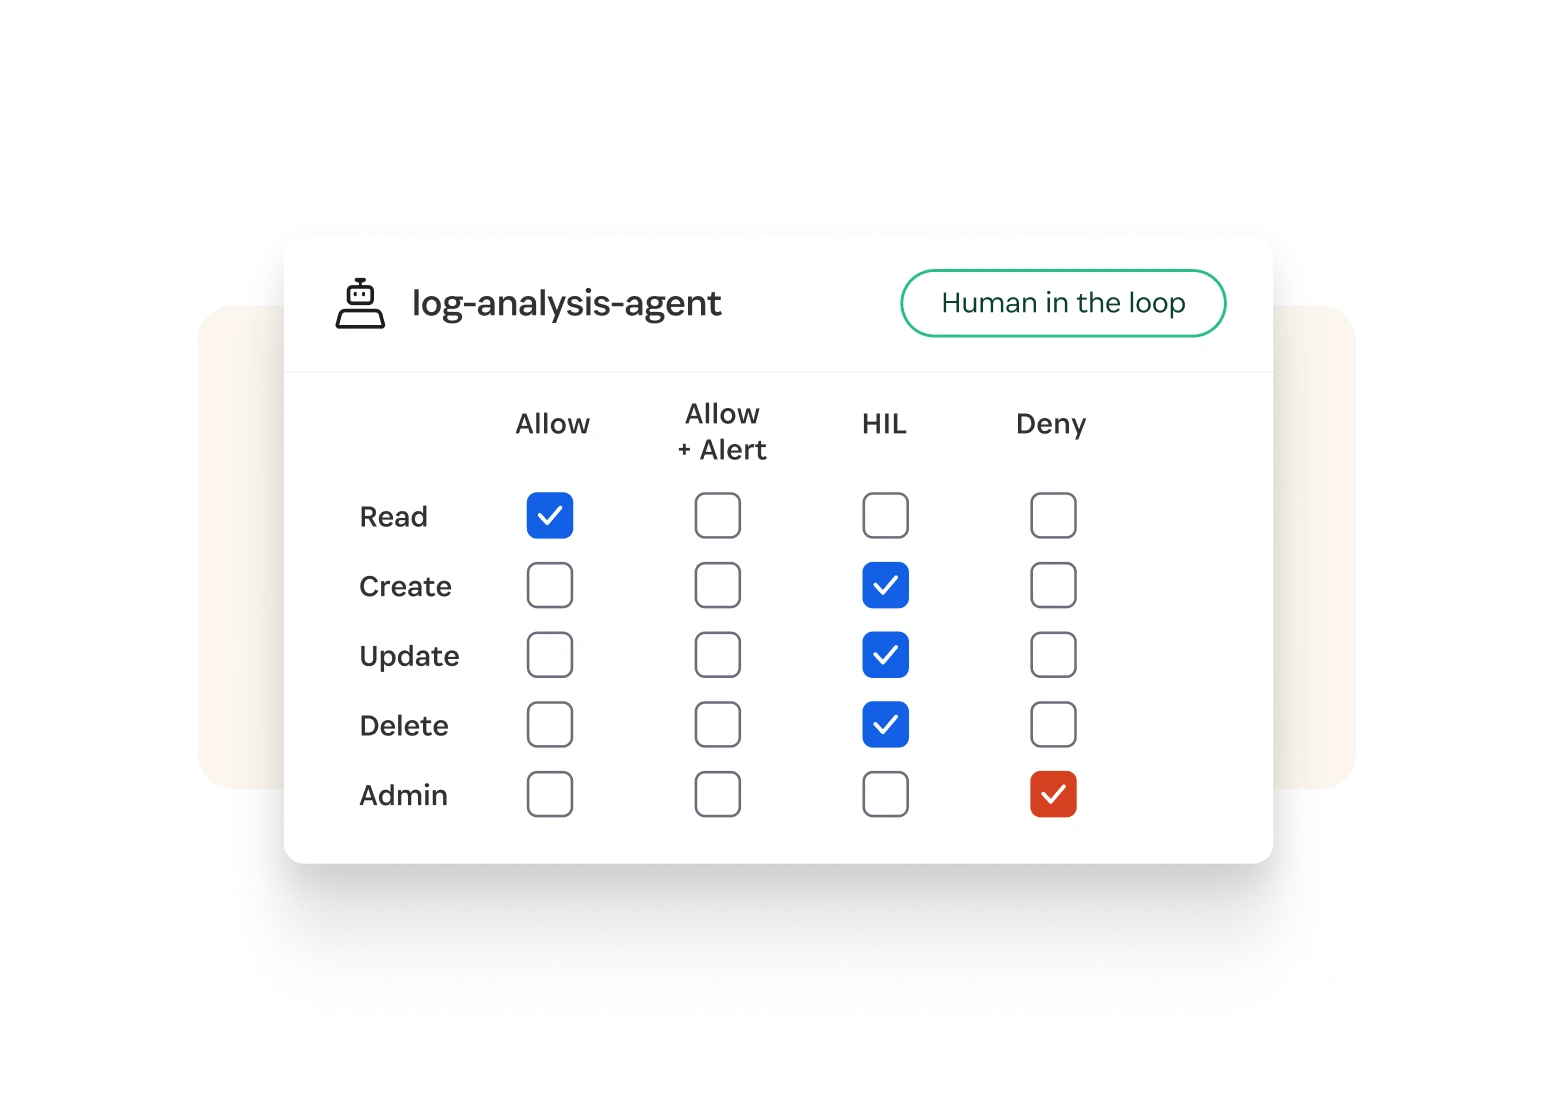
AI Agent Control
- Task-specific identities with no standing access
- Real-time monitoring via IBAC
- Smaller blast radius across every agentic workflow
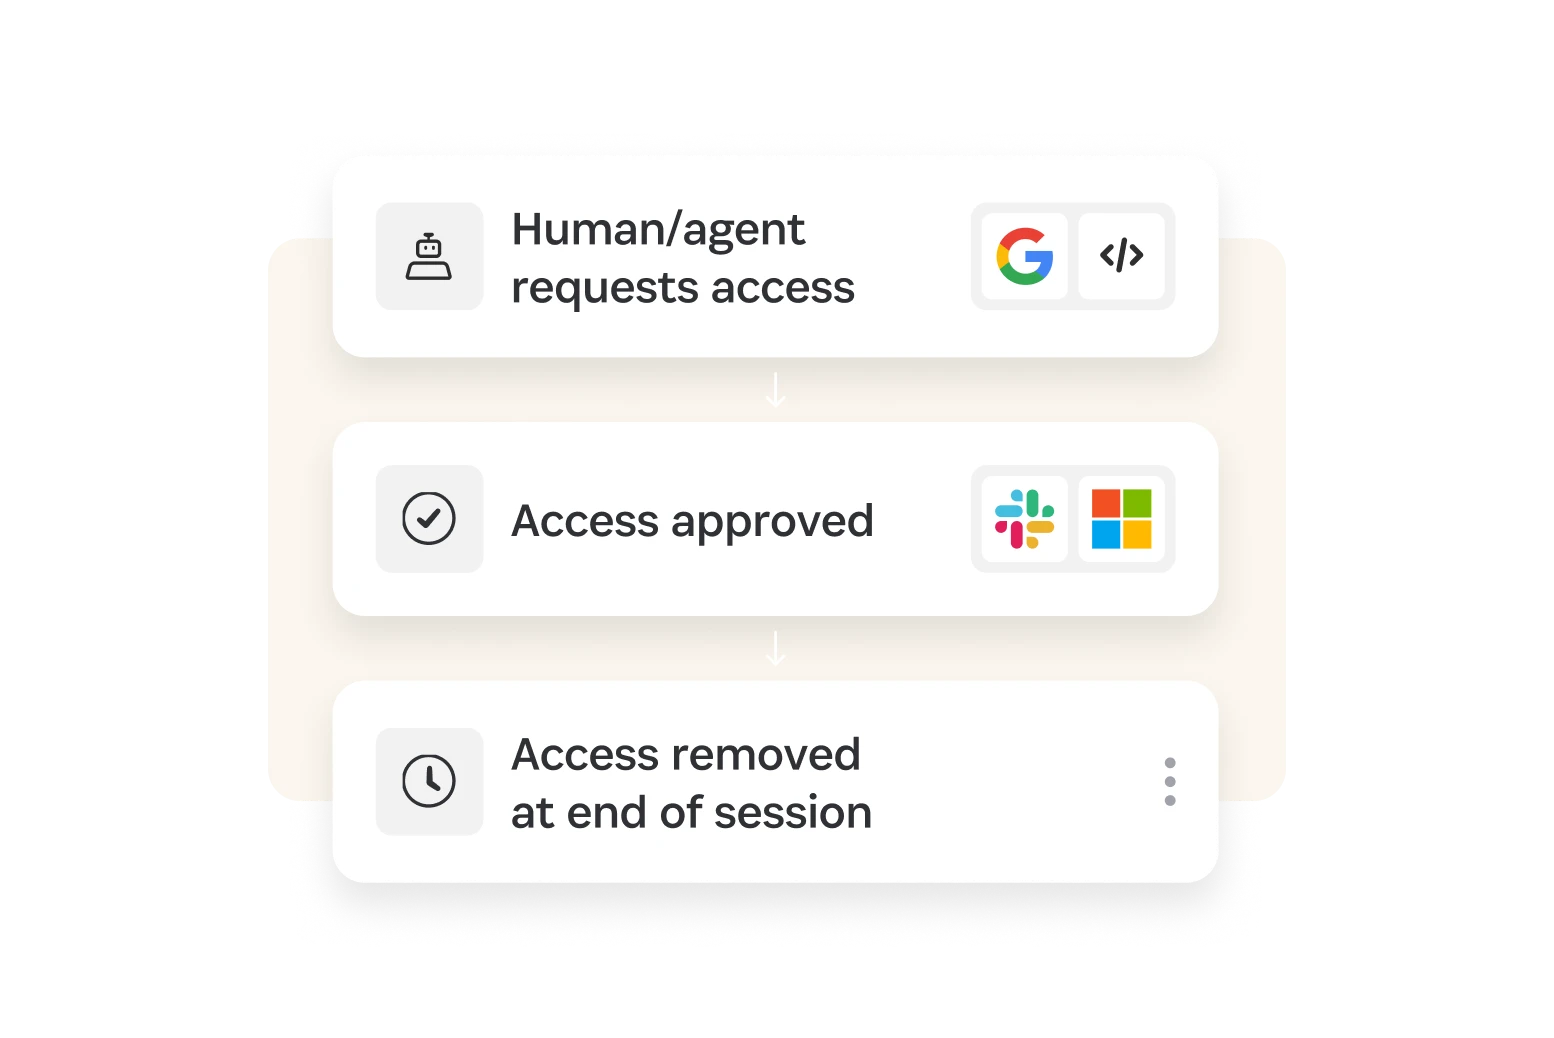
Just-in-Time Access
- Precisely scoped permissions across environments
- Request access from Slack teams, the CLI or MCP, integrated with with ITSM tools
- Policy-based auto-approval for low-risk requests
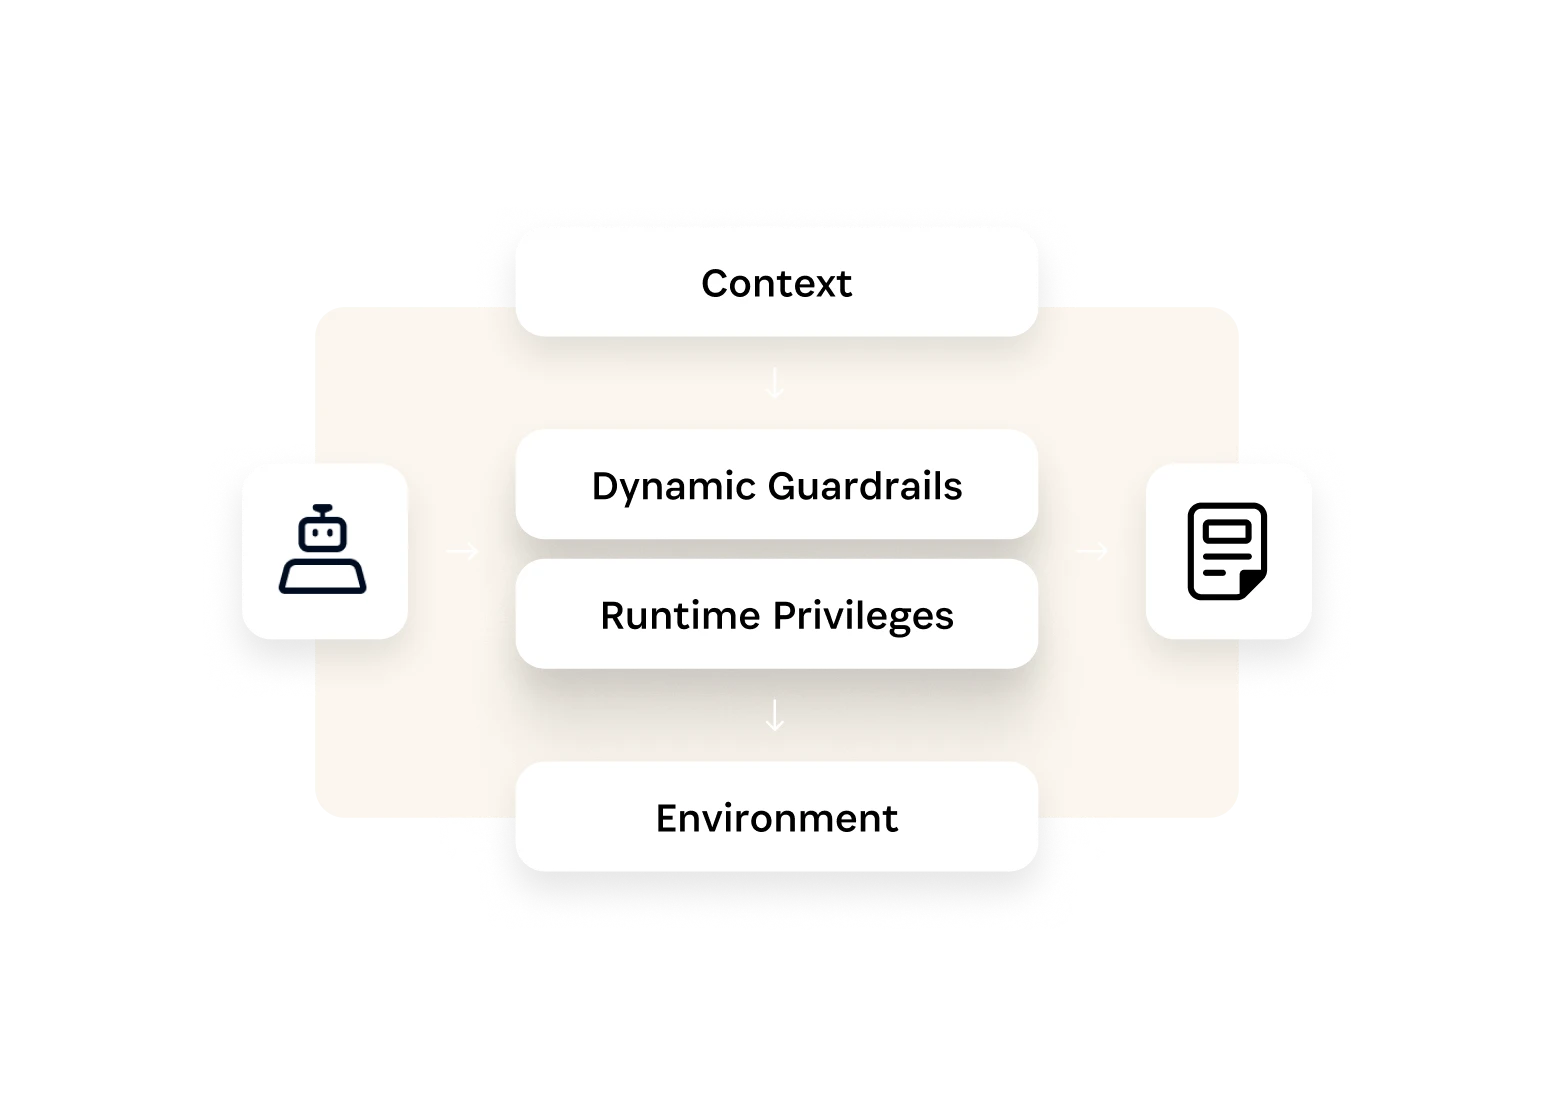
Dynamic Guardrails
- Business context factors into every access decision
- Risk-based enforcement across cloud, K8s, and databases
- Policies can be easily modified or augmented as your environment grows
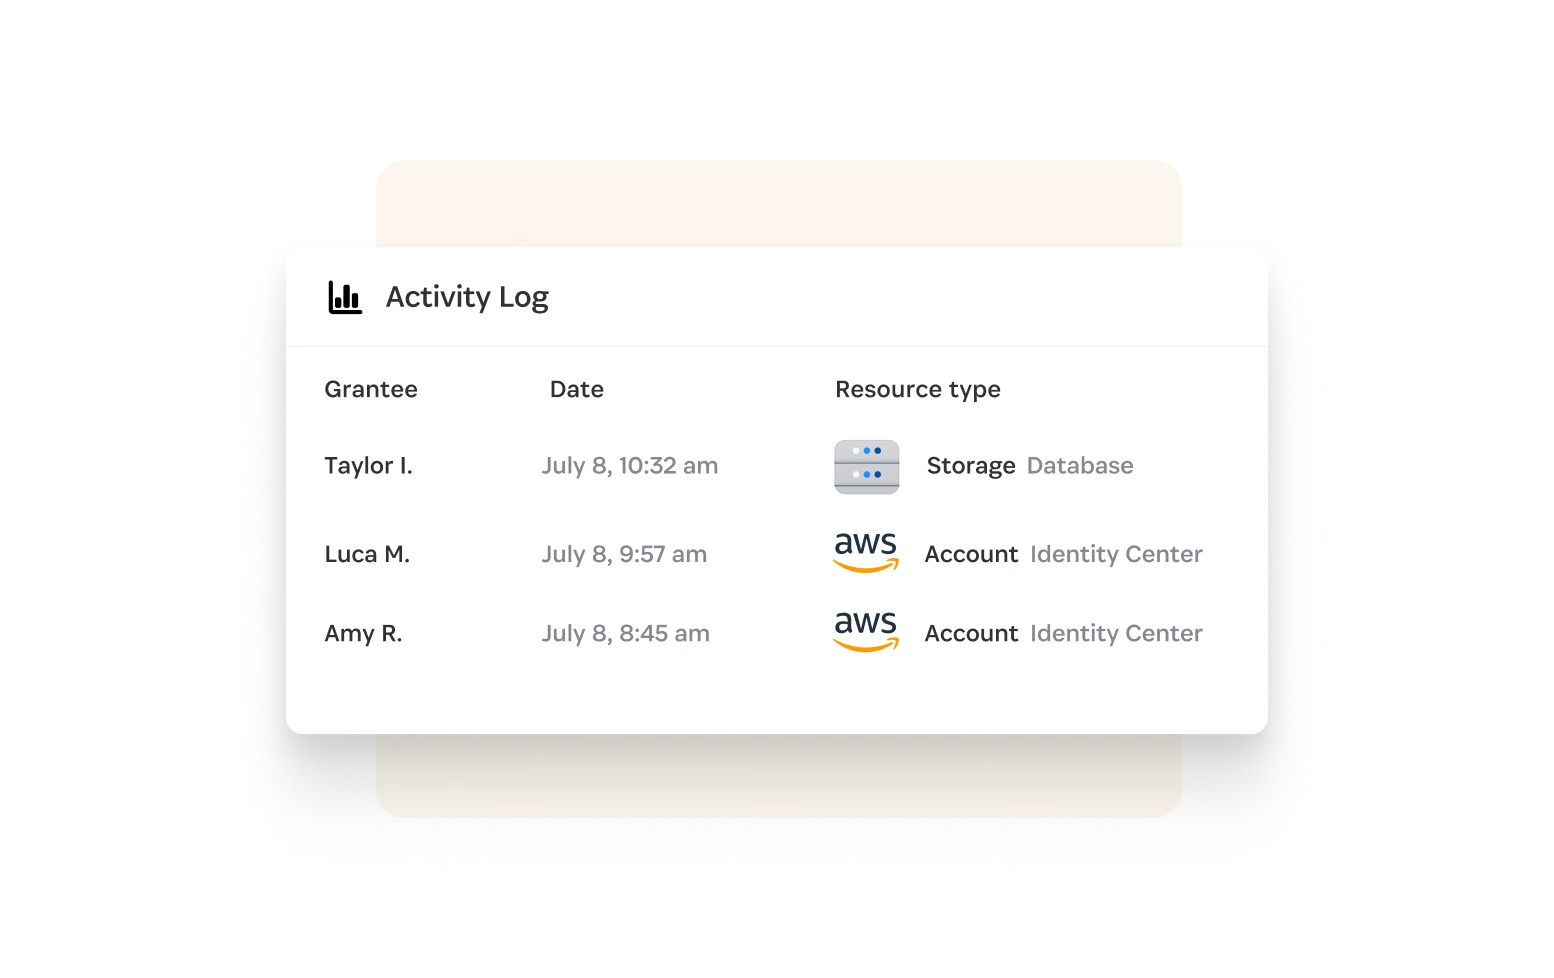
Audit and Compliance
- Compliance reporting
- Automatic Anomaly Detection for anomalous patterns
- Full business context on every access event
1Password recognized in the 2026 Gartner® Magic Quadrant™ for Privileged Access Management
1Password Privileged Access was named an Honorable Mention.
Privileged Access is part of the Unified Access Platform
The platform that discovers, secures, and audits access across every identity.
Privileged Access FAQs
What is just-in-time privileged access?
Just-in-time access means delivering the right access to the right identity, and only at the moment it's needed. It’s created on request, scoped to the specific task, and removed when the session ends.
What does 1Password Privileged Access do?
How does 1Password Privileged Access eliminate standing privileges?
How does 1Password Privileged Access secure AI agents?
Does 1Password Privileged Access require proxies, bastion hosts, or per-server agents?
How does 1Password Privileged Access fit into the 1Password® Unified Access platform?
How does 1Password Privileged Access support audit and compliance?
Eliminate standing access
See just-in-time access provisioned and removed across cloud, database, and K8s environments.